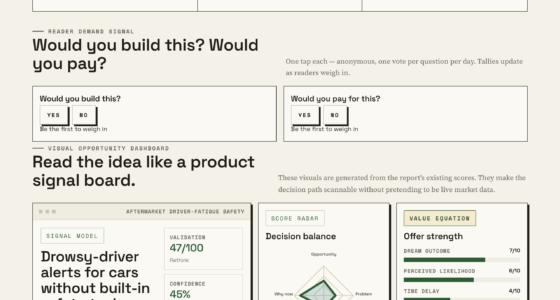
📊 Full opportunity report: A Better Way To Govern Autonomous AI Agents on IdeaNavigator AI — validation score, market gap, and execution plan.

Get business pricing on office and shipping supplies
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
TL;DR
IdeaNavigator AI has outlined a proposed security workflow that would require autonomous agents to obtain a signed, single-use authorization before taking specified high-risk actions. The concept has not been presented as a deployed product or validated result; its suggested first test is to place one team’s refund or deletion endpoint behind a proxy for a month.
According to a product proposal published by IdeaNavigator AI, a proxy would require an autonomous AI agent to request single-use approval for each high-risk API action, with policy checks and an audit record for each grant or denial. The concept is aimed at platform engineers deploying agents that can take real-world actions, but the material describes a proposed workflow—not a launched product, measured security result or confirmed customer deployment.
In its proposal, IdeaNavigator AI describes a proxy that would sit between an agent and a high-risk service, such as an API that issues refunds or deletes records. Before acting, the agent would submit a request specifying the exact action and its arguments. The proxy would apply policy rules and, if the request is allowed, issue a signed token intended for one use. The proposal says the system would log both approvals and denials for later review.
The proposal identifies a risk it is intended to address: teams may give agents broad API tokens that allow them to perform actions without a separate, scoped approval at the moment of execution. It gives prompt injection or a reasoning error as possible paths to an agent sending a refund, deleting data or emailing a customer. These are examples of potential harm cited in the proposal, not reported incidents tied to a particular organization.
For an initial test, IdeaNavigator AI recommends wrapping one team’s refund or deletion endpoint with the proxy for one month. The proposal says the team would require per-action tokens and compare blocked unsafe actions and added latency with an unscoped baseline. It also suggests usage-based charges for each authorized action, alongside a platform fee for policy controls and an audit dashboard. No pricing, performance figures or test results are provided in the material.
PROPOSED SECURITY WORKFLOW · IDEANAVIGATOR AI
A Better Way To Govern Autonomous AI Agents
A product proposal would put a policy checking proxy between an AI agent and a high risk API, requiring a signed, single use authorization for each permitted action. It describes a concept and a possible test, not a launched product or proven safeguard.
Approve the action at the moment it happens.
Scope each authorization to a specific request and its arguments.From broad credentials to action checks
The proposal targets standing API access: a broad credential may let an agent take consequential actions without a separate decision at execution time. A proxy could create a defined enforcement point for policy checks and an audit trail.
Broad permission
An agent’s credential may allow actions such as issuing refunds or deleting records whenever the agent calls the API.
Consequential actions
Refunds, record deletion, and customer emails are examples of possible harm after a prompt injection or reasoning error.
Risk, not incidents
These are hypothetical pathways cited by IdeaNavigator AI, not reported events tied to a named organization.
One decision for each high risk action
The agent requests approval for a specific operation and arguments. If policy allows it, the proxy returns a token intended for one use and records the outcome.
Name the action
Submit the intended API action with its arguments.
Evaluate the request
Apply rules to decide whether this request is permitted.
Issue one token
For an allowed action, issue a signed token intended for one use.
Log the outcome
Record grants and denials for later review.
Controls and visibility at the point of action
Access control and audit serve different purposes. Policy checks may reject requests outside defined rules; logs may help operators review what agents attempted. The proposal does not show that the design prevents every injection or reasoning error.
Check before execution
A policy decision could stop an action that falls outside the team’s configured limits.
Keep both outcomes
Records of approvals and denials could give teams a view of allowed and rejected requests.
Rules must match reality
Value depends on accurate policies and reliable validation of the requested action and arguments.
Test one endpoint for one month
IdeaNavigator AI suggests routing one team’s refund or deletion endpoint through the proxy, then comparing the results with an unscoped baseline.
A focused operational trial
Require per action tokens, record approvals and denials, and observe the proxy in a real workflow. The proposal says no trial has begun and provides no results.
+ added latency
What a team would need to learn
The proposal outlines a workflow, but leaves key implementation and readiness questions unanswered.
Is there a working proxy? The proposal does not report a build, supported policy rules, or a release schedule.
Does execution match approval? It is unclear how the proxy would confirm the API action matches the authorized request.
What happens on retries or outages? Expiration, changed arguments, retries, and proxy or policy service failures are unspecified.
How well does it perform? No latency, false approval, false denial, or blocked action figures are provided.
| Question | What the proposal says | Evidence status |
|---|---|---|
| Product availability | Describes a proposed authorization workflow and proxy. | Unknown · no launch reported |
| Customer deployment | No participating team or confirmed customer is identified. | Not reported |
| Security and performance | Suggests a trial measuring blocked unsafe actions and latency. | No test results |
| Commercial model | Usage based charges plus a platform fee are suggested. | No prices or demand evidence |
Key questions, plainly answered
What is the proposed system?
A proxy between an AI agent and a high risk API. It checks policy, issues a signed single use token for an allowed action, and logs grants and denials.
Is it deployed or available?
The material describes a proposal and suggested trial. It reports no product launch, customer deployment, or completed test.
What problem does it target?
Broad, standing API credentials that may allow consequential actions without a separate approval for each operation.
How could it be tested?
Place one refund or deletion endpoint behind the proxy for a month and compare blocked unsafe actions and added latency with an unscoped baseline.
A concept with a proposed next step
Per action approval
Replace broad access at the point of action with scoped authorization.
One endpoint
Start with a team’s refund or deletion API.
One month
Observe policy decisions and operational impact.
Not yet reported
No measured outcome is provided in the proposal.
Reducing Agents’ Standing API Access
For organizations that let software agents change records, move money or contact customers, the design described in IdeaNavigator AI’s proposal shifts authorization from a broad credential issued in advance to an individual decision at the point of action. That could make it easier for teams to set limits on what an agent may do and to review what it attempted, including requests that were rejected.
The distinction matters because access control and audit are separate needs. A policy check could stop an action that falls outside defined rules, while a record of grants and denials could help operators investigate how an agent behaved. However, the proposal does not establish that the proxy would prevent prompt injection or reasoning mistakes in every case. Its value would depend on how accurately policies describe permitted actions and whether the proxy can reliably validate the requested action and arguments.
The proposed one-endpoint trial also reflects the operational trade-off. A per-action check may add a control layer, but it could add latency or complicate workflows that depend on quick API responses. Measuring both blocked unsafe actions and delay would help a team decide whether the added oversight is useful for a particular endpoint. The proposal offers a test plan, not evidence that the benefits outweigh the costs.
Popular right now

Shark Navigator Lift-Away Upright Vacuum (NV360)

Samsung 42-Inch S90H OLED 4K Smart TV Bundle

Roborock Q7 M5+ Robot Vacuum and Mop
As an affiliate, we earn on qualifying purchases.
From Broad Tokens to Action Checks
IdeaNavigator AI’s proposal is aimed at platform engineers responsible for deploying agents that call tools and act through APIs. The proposal characterizes these systems as moving into production and argues that conventional OAuth scopes can be coarse: they may grant standing access to a service rather than require time-limited approval for each operation. That framing comes from IdeaNavigator AI; its material includes no market-wide adoption figures or independent assessment of OAuth implementations.
Rather than replace an agent framework or secure every API at once, the proposal recommends focusing a first version on one high-risk API. A proxy could provide a defined enforcement point, check each request against policy and keep a log. The approach is presented as a focused security-infrastructure concept, with a month-long endpoint trial as its suggested initial validation step.
Key Questions Before Deployment
IdeaNavigator AI reports no implementation or test findings in its proposal. It is unclear whether a working proxy has been built, which policy rules it would support, or how it would confirm that the action executed by the API matches the action described in the authorization request. The proposal also does not specify how tokens would expire, how retries or changed arguments would be handled, or how the system would respond if the proxy or policy service were unavailable.
The material provides no measurements for latency, false approvals, false denials or the number of unsafe actions that a trial might block. It does not identify a participating team, a product vendor, a release schedule or confirmed customers. Its commercial model is described at a high level, with no prices or evidence of buyer demand. Those details would be needed to judge both technical readiness and market viability.
A One-Month Endpoint Trial
IdeaNavigator AI’s proposal recommends a controlled trial on one team’s refund or deletion endpoint. The team would route agent requests through the proxy, require a signed, single-use token for each permitted action and record approvals and denials. It would then compare blocked unsafe actions and added latency with the endpoint’s unscoped baseline.
That test could provide an initial indication of whether per-action controls are practical for a specific workflow, but IdeaNavigator AI does not say that a trial has begun or when results might be available. Until a deployment and its measurements are reported, the approach remains a product idea rather than a demonstrated safeguard. The proposal is available from IdeaNavigator AI.
Source: IdeaNavigator AI
Key Questions
What is the proposed per-action approval system?
In IdeaNavigator AI’s proposal, it is a proxy between an AI agent and a high-risk API. The agent would request a signed, single-use token describing a specific action and its arguments; the proxy would check policy and log whether it grants or denies the request.
Is this system already available or deployed?
IdeaNavigator AI’s material describes a proposed workflow and a suggested trial. It does not report a product launch, a deployed customer system or completed testing.
What problem is the proposal intended to address?
IdeaNavigator AI says the proposal targets the risk of giving an agent a broad, standing API credential that can be used to take consequential actions without approval for each one. The proposal cites refunds, record deletion and customer emails as examples of actions that could cause harm if an agent is manipulated or makes an error.
How would the proposal be tested?
IdeaNavigator AI suggests placing one team’s refund or deletion endpoint behind the proxy for one month. The team would compare blocked unsafe actions and added latency against an unscoped baseline; the proposal reports no results from such a test.
What is not yet known about the approach?
The proposal reports no performance or security results, implementation details, confirmed customers or prices. It is also unclear how the proxy would handle failures, retries and cases where the API action differs from the authorization request.
Source: IdeaNavigator AI